Users & Groups
ClearML Hosted Service users can add users to their workspace.
Additionally, administrators on the ClearML Enterprise plan can define user groups to control access privileges, and create service accounts for automations.
Inviting new teammates is only available on the ClearML Hosted Service.
Users
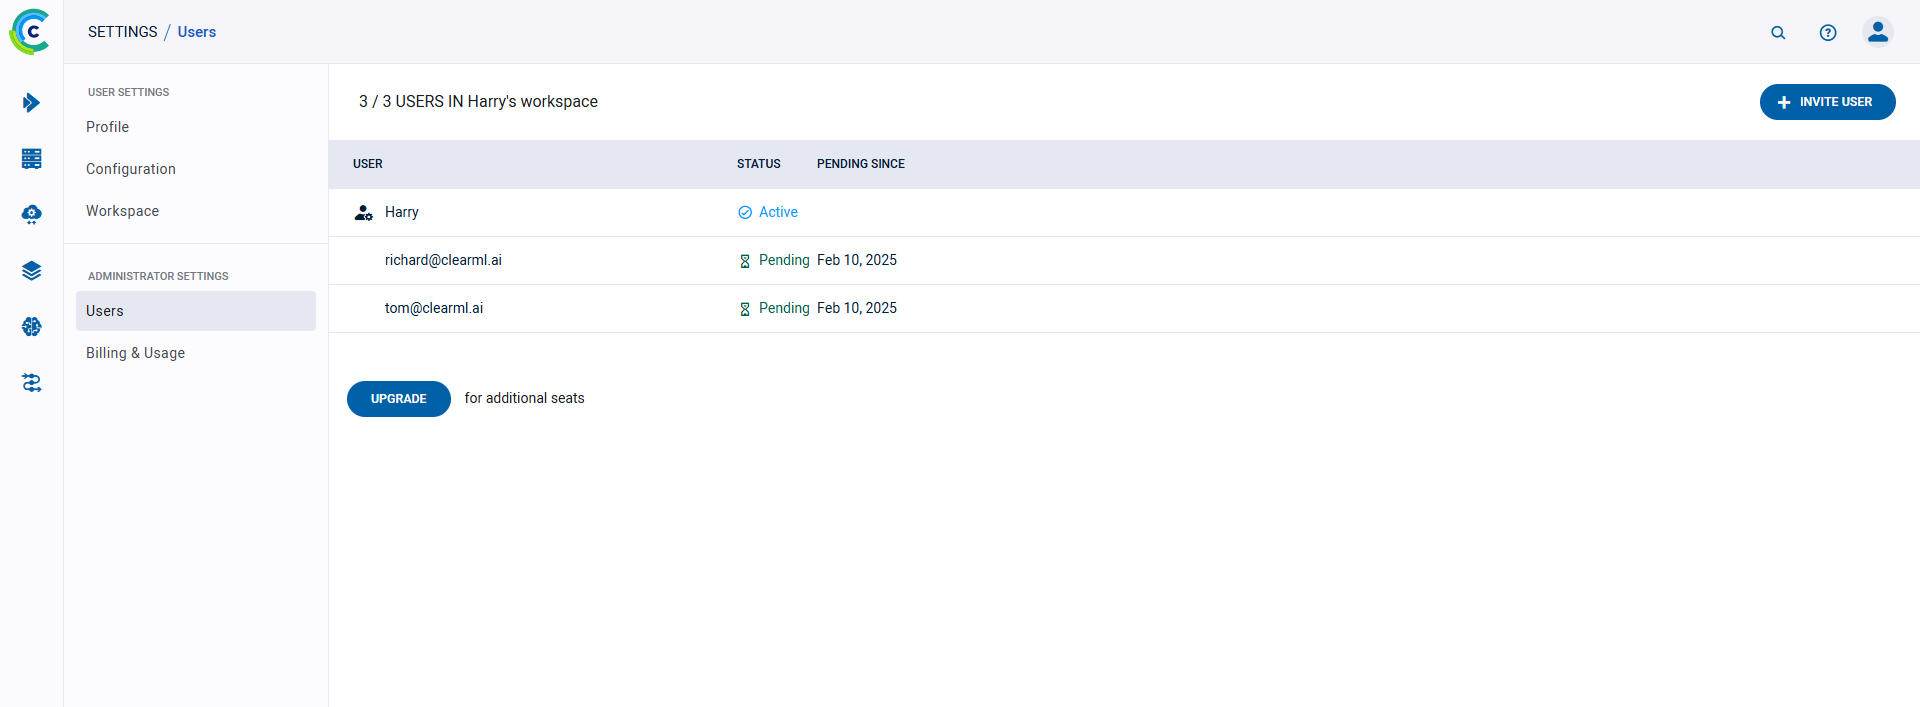
The USERS table lists workspace members and details, and shows whether the maximum number of members has been reached.
Use the search bar  to find a specific user by their name, email, or user ID.
Free/Pro Service
The Free/Pro service's USERS table includes the following information:
- Username
- User status (
ActiveorPending) - If the user's invitation is pending, the date the user was added
Enterprise Offering
The ClearML Enterprise USERS table includes the following information:
- Username
- Groups: The user groups the user belongs to
- User ID
- Login: Last time a user logged in to the system, and the sign on provider that was used
- API Cred. Used: Last time a user’s API credentials were used to generate an authorization token
- UI Activity: Last time a user accessed the ClearML UI
Inviting New Teammates
To invite a user to your workspace, press the + INVITE USER button, and input the email in the dialog that pops up. Once invited, the added users can immediately access your workspace.
Removing Teammates
To remove a user from a workspace:
- Hover over the user's row on the table
- Click the
 button
Removed users lose access to your workspace's resources (tasks, models, etc.) and their existing access credentials are revoked. Tasks and associated artifacts logged to your workspace by a removed user will remain in your workspace. The user can only rejoin your workspace when you re-invite them.
Service Accounts
Service accounts are available under the ClearML Enterprise plan.
Service accounts are ClearML users that provide services with access to the ClearML API, but not the UI. Administrators can create access credentials for service accounts to use them for different ClearML Agents, automations, and more.
A service account has all the privileges of a normal user in ClearML, with the following limitations:
- Service accounts cannot be used to access the UI
- Service accounts can be used to facilitate running tasks under the identity of each task's owner ("Impersonation").
- Used to run an agent using the command-line, this will allow you to specify the
--use-owner-tokenoption. - Used to run the ClearML Agent Helm Chart, this will allow you to specify
values.agentk8s.useOwnerToken: trueoption. - Used to run an Autoscaler application, this will allow you to make use of the
Apply Task Owner Vault Configurationoption.
- Used to run an agent using the command-line, this will allow you to specify the
When access controls are provisioned, they apply to service accounts the same as for ClearML users. Therefore, in order to use a service account to run an agent in daemon mode, the service account must have access to the queue the agent will service.
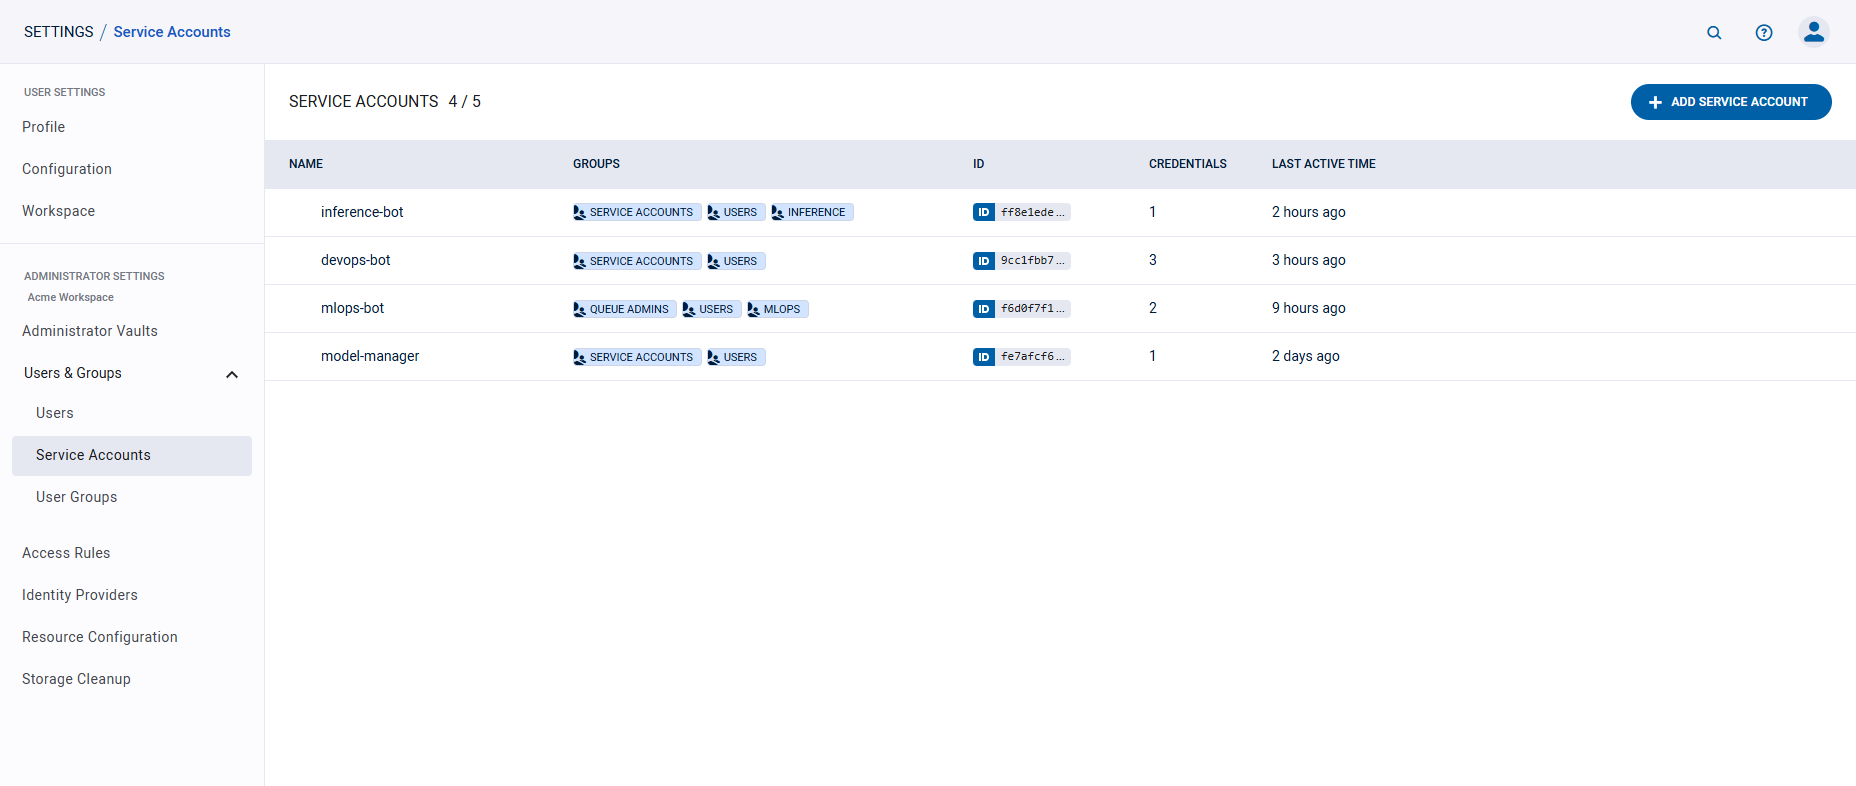
The SERVICE ACCOUNTS table lists workspace service accounts. Each row of the table includes:
- Name - Service account name
- User groups
- User ID
- Credentials - Number of credentials currently available to the account
- Last active time
Use the search bar
to find a specific service account by its name or ID.
Hover over a service account in the table to Edit or Delete it.

Creating a Service Account
To create a service account:
- Click + ADD SERVICE ACCOUNT
- In the ADD SERVICE ACCOUNT modal:
- Input a name for the new account
- Select
Allow impersonationto allow the service account to assume the identity of the owners of the tasks it is running. - Select
Set as Adminto grant the service account administrator privileges. See Setting a Service Account as Administrator for details on enabling admin service accounts. - Set the expiration period for the service account’s initial set of credentials
- Click Save
Service accounts are members of the Users group, meaning they can access the resources available to all users. When
impersonation is enabled, a task run by the service account (i.e. by an agent or autoscaler using the service accounts'
credentials) is executed as if by the owner of the task, meaning it will have access to the task owner's configuration
vaults and to the resources that the task owner has access to. Impersonating an admin user does not mean the task's code
will have admin privileges (see Setting a Service Account as Administrator).
In case impersonation is not enabled:
- If you run an agent with
--use-owner-tokenthen the agent will fail. - If you run an agent without
--use-owner-token, the task will run with the service account's access rules, so make sure the account uses resources it has access to
When a service account is created, an initial set of credentials is automatically generated. The dialog displays new credentials, formatted as a ready-to-copy configuration file section.
Setting a Service Account as Administrator
You can grant a service account administrator privileges, giving it the same access and capabilities as an admin user.
Prerequisite: Enable Admin Privileges for Service Accounts
To allow admin roles to be assigned to service accounts, you must enable support for admin service accounts on the server in one of the following ways:
- Set as an environment variable: Set
CLEARML__services__organization__allow_service_user_admins=truein theapiserverservice environment - Edit the services/organization.conf file: Set
allow_service_user_admins: true
Assigning Admin Role to a Service Account
To assign an admin role to a service account:
- Go to the Service Accounts table.
- Click the service account you want to modify to open its details panel.
- Select Admin toggle to grant administrator access.
Service Account Credentials
To generate new credentials for a service account:
- Click the account's row on the table, which opens the editing panel
- Click Create new credentials
- In the Create Credentials modal:
- Under
Label, enter a descriptive name for the credentials - Set the expiration period for credentials
- Under
The dialog displays new credentials, formatted as a ready-to-copy configuration file section.
To revoke a set of credentials:
- In the editing panel, hover of the relevant credential's row
- Click the button
AI Application Gateway Endpoint Access
The AI Application Gateway enables external access to ClearML tasks and applications. The gateway is configured with an endpoint or external address (ingress), accessible from outside ClearML.
Generate tokens providing API access to the AI Application Gateway endpoints:
- Click Generate a Token
- Under
Label, enter a descriptive name for the token - Under
Expiration, enter the number of days the token should remain valid - Click
Generate, which creates a token and copies it to your clipboard
The AI Application Gateway Table displays all tokens available to the service account, and the following details:
- Token label
- Creation time
- Expiration time
To revoke a token, hover over the token's row and click .
Service Account Configuration Vault
Use a service account’s configuration vault to store ClearML configuration entries that can extend the ClearML configuration file of any ClearML Agents or ClearML SDK running with the service account's credentials.
Vault entries will extend the configuration in the ClearML configuration file if they don't yet exist, and override values for those already present in the file.
Fill in values using any of ClearML supported configuration formats: HOCON / JSON / YAML.
To edit vault contents:
- Click on the relevant service account to open its details panel
- Click EDIT on the configuration vault
- Insert / edit the configurations in the vault
- Press OK
To apply vault contents:
- Click the toggle atop the vault to enable / disable the configurations
- Once enabled, the configurations will be merged to the configuration file during ClearML and ClearML Agent usage
In addition to the service account-specific configuration vault, administrator vaults can also be applied to service accounts. See all the vaults applied to the account in the Applied administrator vaults below the configuration vault.


Deleting Service Account
Deleting a service account will revoke its credentials, causing agents using the account's credentials to fail. Tasks and associated artifacts logged to your workspace by a service account will remain in your workspace.
To delete a service account:
- Hover over the account's row on the table
- Click the button
User Groups
User groups are available under the ClearML Enterprise plan, as part of the Access Rules feature.
Administrators can define user groups, which can be used for access privilege management. Users can be assigned to multiple user groups.
The system includes three pre-configured groups that can't be removed:
Users- All users (including service accounts). Can't be modifiedAdmins- Have RW access to all resources (except queue modification), and can grant users / user groups access permissions to workspace resourcesQueue admins- Can create / delete / rename queues
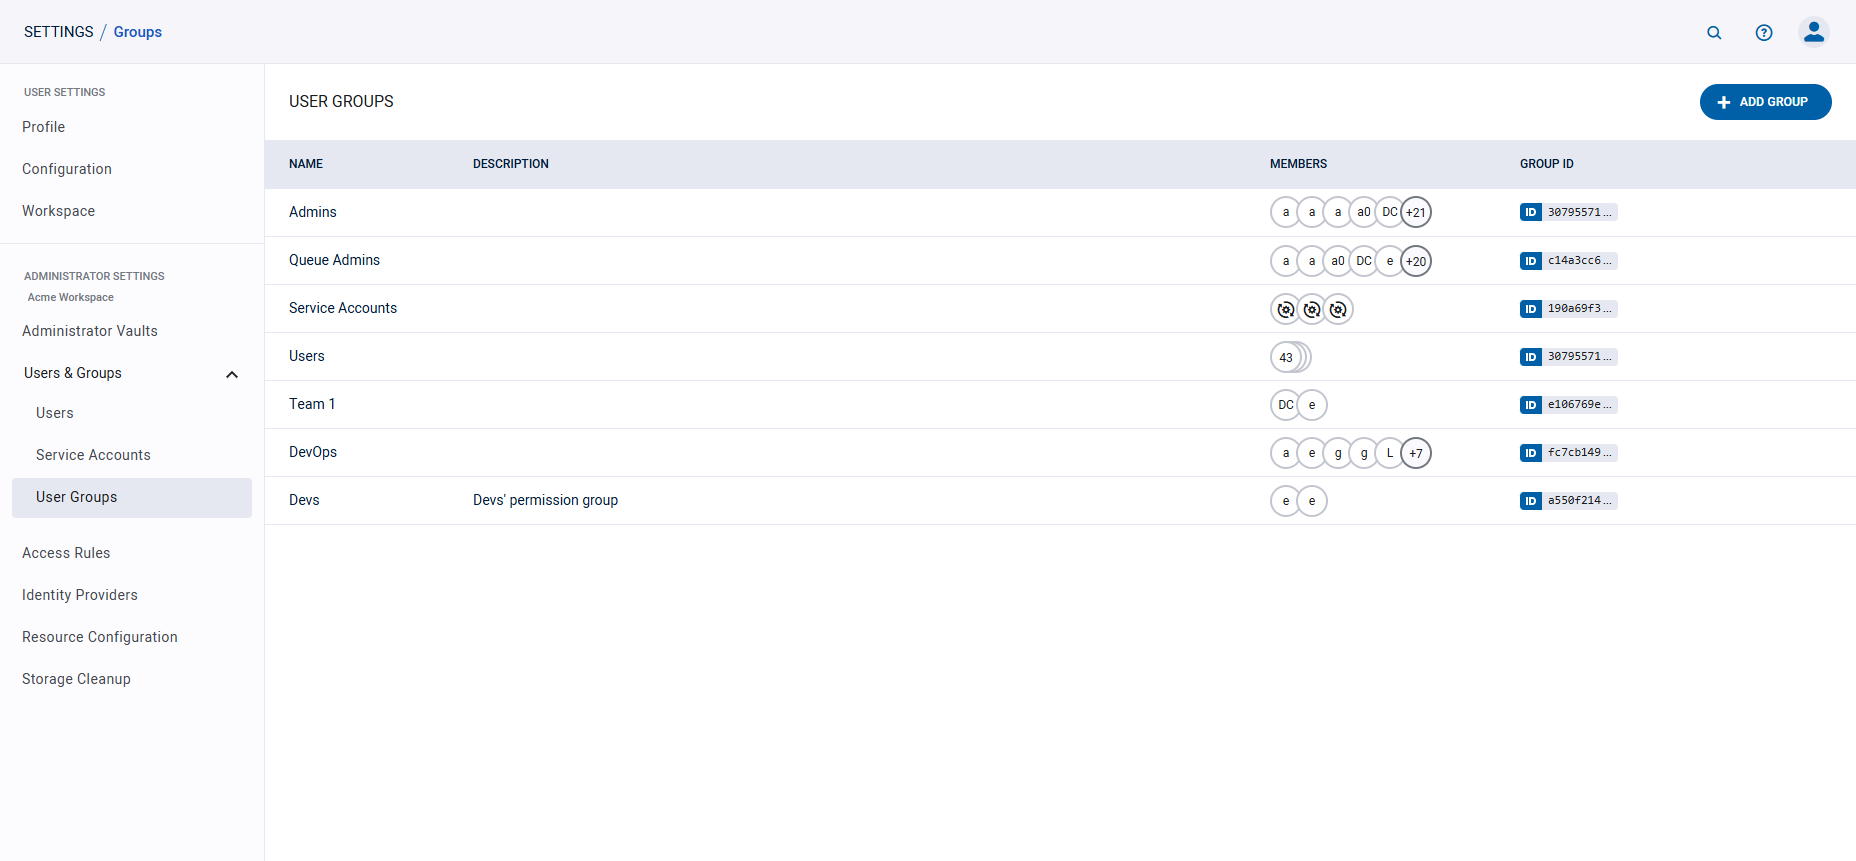
The user group table lists all the active user groups. Each row includes a group's name, description, member list, and ID.
Use the search bar
to find a specific user group by its name, description, or ID.

Creating a User Group
To create a user group:
- Click + ADD GROUP
- In the dialog, add a group name and description
- Add members to the group. When clicking the input box, a list of workspace members appears, from which group members
can be selected. Filter the list by typing part of the username. To remove a member, hover over a user's row and click
the button
- Click SAVE


Editing a User Group
To edit a user group:
- Hover over the user group's row on the table
- Click the
 button
- Edit the group's name and/or description
- Edit group members (see details here)
- Click Save
Deleting a User Group
To delete a user group:
- Hover over the user group's row on the table
- Click the button
When a user group is deleted, its members will lose the access privileges that had been granted to the group (unless otherwise provided individually or to another group they are members of).