Administrator Vaults
Administrator vaults are available under the ClearML Enterprise plan.
Administrators can define multiple configuration vaults which will each be applied to designated user groups. There are three types of vaults:
To apply its contents, a vault should be enabled in the Administrator Vault Table.
Client Configuration (Agent/SDK/CLI)
Client configuration vaults extend and/or override entries in the local ClearML configuration file where a task is executed. Vault values will be applied to tasks run by members of the designated user groups.
New entries will extend the configuration in the local ClearML configuration file. Most existing configuration file entries will be overridden by the vault values.
The following configuration values are machine and/or agent specific, so they can't be set in a configuration vault:
agent.cuda_versionagent.cudnn_versionagent.default_pythonagent.worker_idagent.worker_nameagent.debug
To create a Client configuration vault:
- Click + Add Vault
- Fill in vault details:
- Vault name - Name that appears in the Administrator Vaults table
- User Group - Specify the User Group that the vault affects
- Target - Vault type. Select
Client (Agent/SDK/UI) - Format - Specify the configuration format: HOCON / JSON / YAML.
- Fill in the configuration values (click
 to view configuration file reference). To import an existing configuration file, click
 .
- Click Save
UI Storage Credentials
UI storage credential vaults configure UI access to cloud storage credentials for a designated group of users.
To create a vault:
- Click + Add Vault
- Fill in vault details:
- Vault name - Name that appears in the Administrator Vaults table
- User Group - Specify the User Group that the vault affects
- Target - Vault type. Select
UI storage credentials - + Add access keys - Enter storage credentials (see Browser Cloud Storage Access)
- Click Save
SSH Server
SSH Server Vaults configure SSH keys for SSH sessions spun up through the SSH Session application or ClearML Session by users in the user groups assigned to the vaults.
- The private keys (
ssh_host_*_key) are stored in the vault. - The corresponding public keys (
ssh_host_*_key__pub) are installed on the SSH server to allow clients to verify the server’s identity.
To create an SSH server vault:
- Click + Add Vault
- Fill in vault details:
- Vault name - Name that appears in the Administrator Vaults table
- User Group - Specify the User Group that the vault affects
- Target - Vault type. Select
SSH Server - Add SSH keys. For example:
{"ssh_host_ecdsa_key": "-----BEGIN EC PRIVATE KEY----- …. -----END EC PRIVATE KEY-----\n","ssh_host_ed25519_key": "-----BEGIN OPENSSH PRIVATE KEY----- …. -----END OPENSSH PRIVATE KEY-----\n","ssh_host_rsa_key": "-----BEGIN RSA PRIVATE KEY----- … -----END RSA PRIVATE KEY-----\n","ssh_host_rsa_key__pub": "ssh-rsa …","ssh_host_ecdsa_key__pub": "ecdsa-sha2-nistp256 …","ssh_host_ed25519_key__pub": "ssh-ed25519 …"} - Click Save
Administrator Vault Table
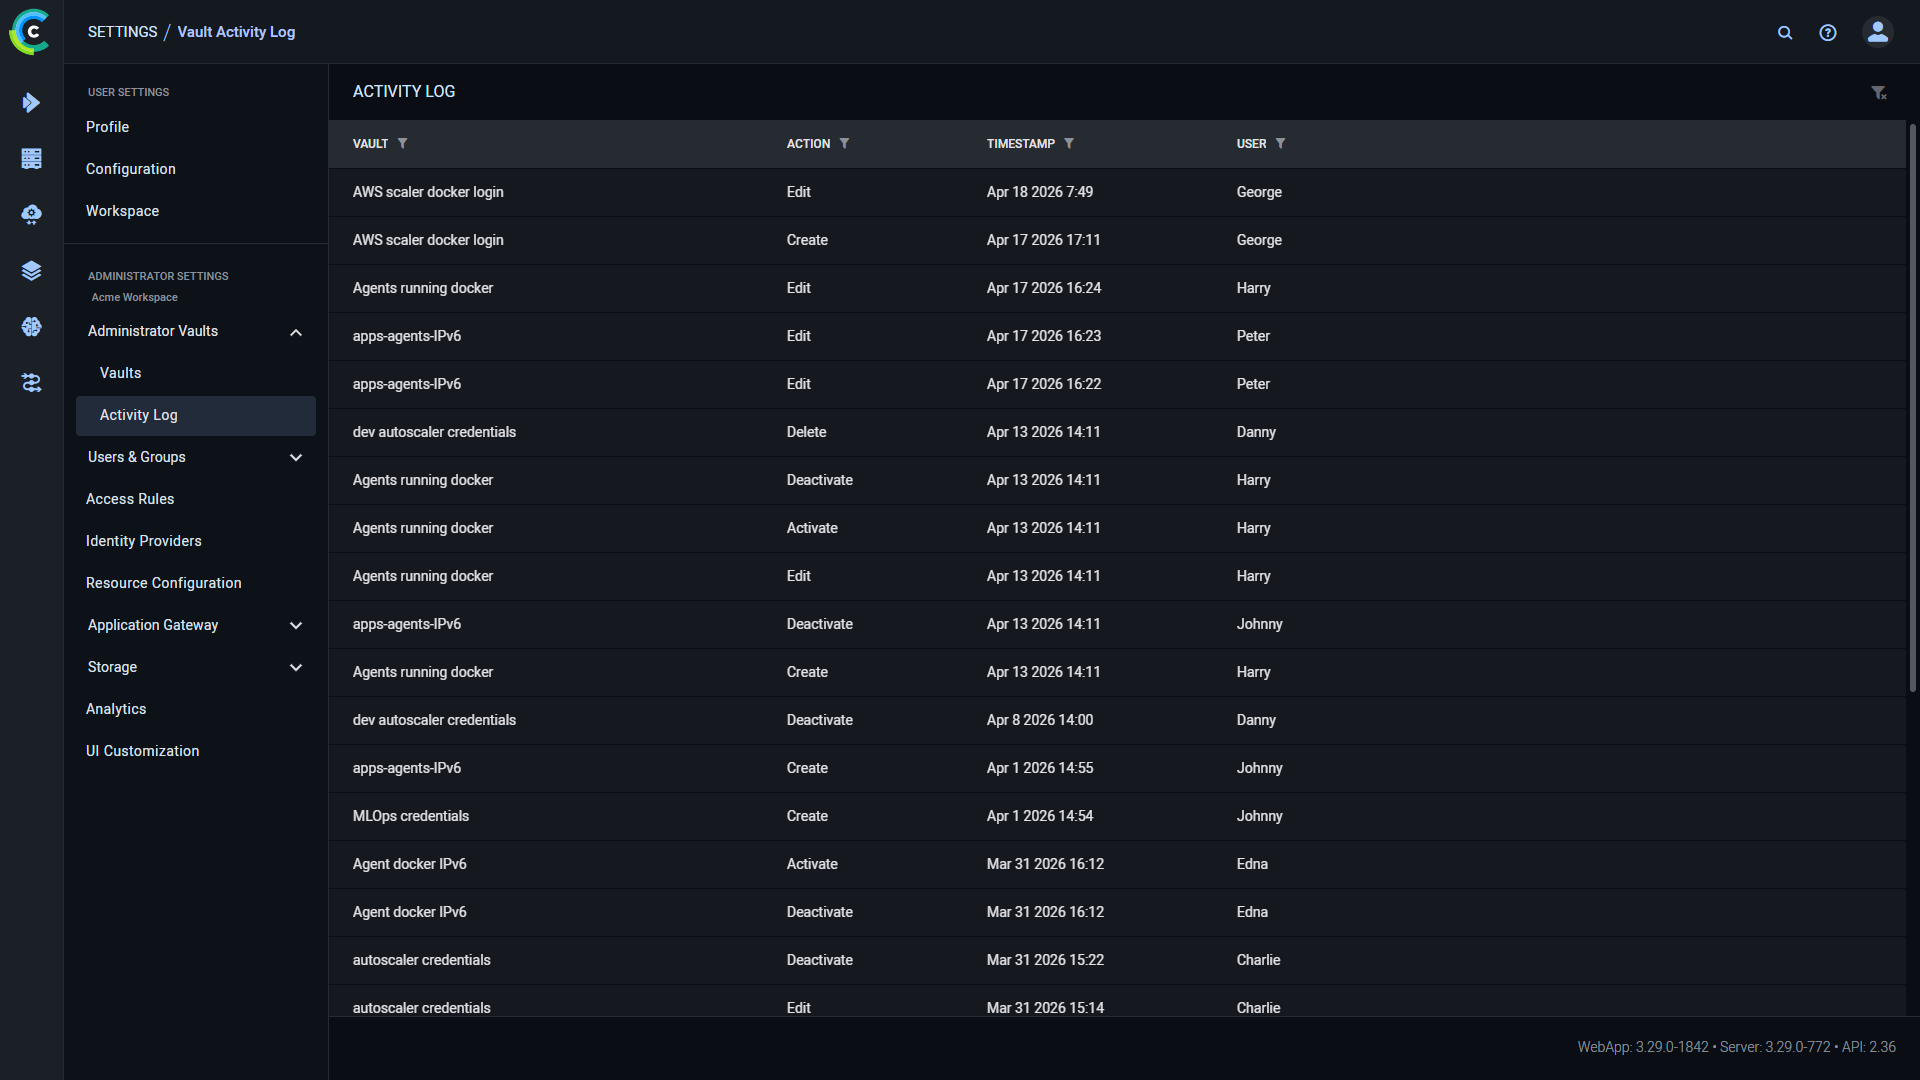
The Administrator Vaults table lists all currently defined vaults, and the following details:
- Active - Toggle to enable / disable the vault
- Name - Vault name
- Target - Type of vault:
Client (Agent/SDK/CLI),UI storage credentials, orSSH server - Group - User groups to apply this vault to
- ID - Vault ID (click to copy)
- Vault Content - Vault content summary
- Update - Last update time
Hover over a vault in the table and click  to access vault actions:
- Download
- Edit
- Delete
- View log - View a history of vault activity: vault action (e.g. activate, deactivate, edit, etc.), acting user, and action time.

Activity Log
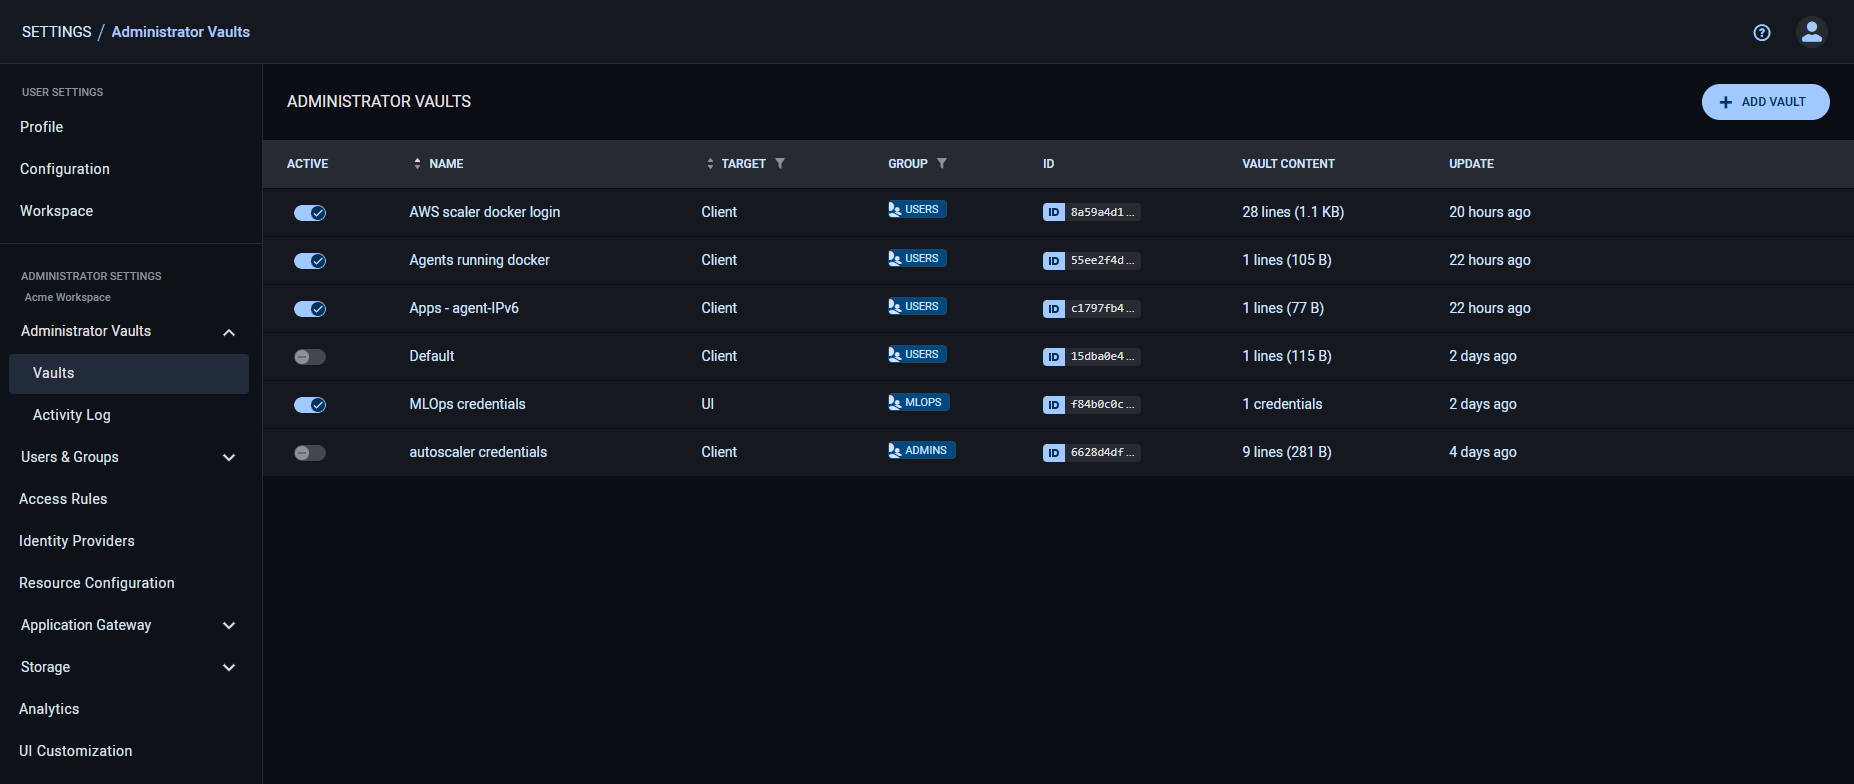
The activity log displays a detailed history of activity across all admin vaults:
- Vault name
- Action: Operation performed on the vault
- Create / Delete
- Activate / Deactivate
- Edit
- Action time
- User who performed the action.
Use the column filters  to
filter the log by vault name, action, time range, or acting user.